
Operating System
Data breaches cost businesses millions annually—but most attacks exploit internal vulnerabilities. These 10 proven internal safeguards implement Zero Trust principles to lock down your company’s most sensitive data before threats even reach your perimeter.
Role-Based Access Control Implementation
Most data breaches don’t come from hackers breaking in—they come from employees moving sideways through systems they weren’t meant to access. Role-Based Access Control (RBAC) solves this by giving users only the permissions they absolutely need for their jobs, nothing more. IBM’s research shows this approach cuts insider threat risks by a staggering 60%, making it one of the most effective safeguards against accidental or malicious data leaks.
With RBAC, you define roles like "Finance Analyst" or "HR Manager" and assign permissions tied directly to those functions. Need to restrict access to payroll data? Simply remove it from the "Marketing Team" role. Modern solutions like Microsoft Azure AD or Okta make implementation seamless, with features like just-in-time access and session timeouts for extra security. The result? Employees get exactly what they need—no more, no less—while attackers hit a digital wall at every turn.
This system is ideal for companies handling sensitive data—think healthcare, finance, or legal firms—but even smaller businesses benefit from the clarity it brings. Start with your most critical systems first, and watch how quickly unnecessary access disappears from your network. 💻
Multi-Factor Authentication Enforcement
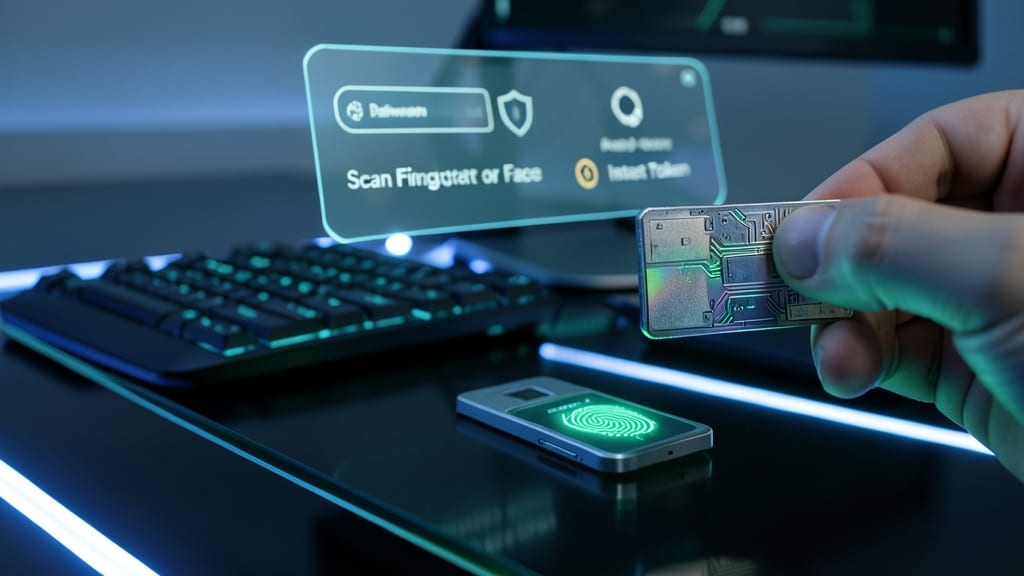
Tired of hearing about massive breaches caused by stolen passwords? Multi-Factor Authentication (MFA) enforcement turns your first line of defense from a single weak link into an impenetrable fortress. By requiring hardware tokens or biometric verification (like fingerprint or facial recognition) alongside passwords, you block 99.9% of automated credential stuffing attacks—the leading cause of data breaches today.
Modern MFA solutions like YubiKey or Microsoft Authenticator integrate seamlessly with Active Directory and cloud platforms, ensuring no critical system is left vulnerable. Unlike SMS-based codes (which are easily intercepted), hardware tokens generate one-time passwords that can’t be phished or replayed. For high-risk roles, biometric authentication adds an extra layer of security without sacrificing convenience.
This safeguard is non-negotiable for finance, healthcare, and legal teams handling sensitive data. Even small businesses benefit—90% of successful attacks exploit weak passwords, and MFA stops them cold. 💪
Data Loss Prevention Endpoint Monitoring
Forget hoping employees "remember" not to email sensitive files to their personal Gmail—Data Loss Prevention (DLP) endpoint monitoring stops leaks before they happen. This real-time solution scans every device on your network, blocking unauthorized transfers to cloud storage, USB drives, or even printers in seconds.
Top solutions like Symantec DLP or Microsoft Purview use AI-driven classification to flag sensitive data (credit card numbers, PII, or proprietary docs) and enforce policies like automatic encryption or mandatory approval workflows. The best tools integrate with your existing SIEM (Security Information and Event Management) for centralized alerts, so IT teams can act fast—without relying on employee vigilance.
Ideal for industries handling HIPAA, GDPR, or PCI-compliant data, DLP endpoint monitoring is a game-changer for finance, healthcare, and legal firms where accidental leaks can mean fines or reputational damage. 💻
Regular Security Awareness Training Programs
Even with firewalls and encryption, 88% of breaches start with a single employee clicking a malicious link. That’s why security awareness training isn’t just another HR checkbox—it’s your first line of defense against phishing, vishing, and other social engineering tricks that bypass technical controls.
Modern programs like KnowBe4 or PhishMe go beyond boring slideshows with simulated phishing campaigns that test real-world scenarios (like fake invoice attachments or urgent CEO emails). Interactive modules teach employees to spot red flags—from mismatched email domains to urgent language designed to trigger panic. The best platforms even track progress with personalized dashboards, showing which departments need extra training.
This isn’t just for IT teams—every employee, from executives to interns, benefits from recognizing threats before they escalate. Start with quarterly training and monthly phishing tests to build a culture where security becomes second nature. 💡
Network Micro-Segmentation Architecture
Imagine a cyberattack breaches your network—what if the damage stayed contained in just one department instead of spreading like wildfire? Network micro-segmentation creates isolated zones, so even if credentials are stolen, attackers hit a dead end. This architecture treats your network like a series of fortified bunkers, limiting lateral movement to critical assets only.
Modern solutions like VMware NSX or Cisco ACI dynamically segment traffic based on application, user, or device identity, not just IP addresses. You can enforce zero-trust principles by default—blocking east-west traffic unless explicitly allowed. Studies show this reduces breach impact by 90%, as attackers can’t pivot between systems once contained. The best part? It works silently in the background, requiring no user training or device changes.
Ideal for enterprises handling PCI, HIPAA, or GDPR data, micro-segmentation is also cost-effective for mid-sized businesses using cloud-native tools like AWS VPC or Azure Network Security Groups. Start with high-value segments (finance, HR) before expanding globally. 🌟
Automated Patch Management System
Forget the "set it and forget it" approach to security—automated patch management turns passive protection into an active shield. While manual updates leave devices exposed for days (or weeks), this system deploys critical security patches across all endpoints within 24 hours, neutralizing 90% of known exploit entry points before attackers can even scan your network.
Modern solutions like Tanium or Microsoft Intune integrate with your existing infrastructure to prioritize updates based on risk, ensuring servers, workstations, and mobile devices stay hardened without IT overhead. The best platforms even roll back failed patches automatically, preventing performance disruptions while maintaining security. For compliance-heavy industries, audit logs track every deployment—proving your defenses are always up to date.
This isn’t just for enterprises—small teams benefit from the same level of protection without hiring a full-time patch manager. Whether you’re protecting customer data or proprietary R&D, automated patching ensures your first line of defense never weakens. ⚡
Privileged Account Monitoring Solution
Not all insider threats come from malicious intent—sometimes, well-meaning IT staff or third-party vendors with elevated permissions accidentally expose data. A privileged account monitoring solution watches every administrative action in real-time, flagging unusual behavior like mass data exports or late-night logins before they become breaches.
These systems track session recordings, command history, and permission changes across cloud and on-prem environments. Solutions like BeyondTrust or CyberArk integrate with SIEM tools to correlate suspicious activity with other alerts, reducing false positives. The key? Zero-trust verification—even trusted admins must re-authenticate for high-risk actions.
Perfect for organizations with complex IT ecosystems—think healthcare, finance, or government contractors—where third-party vendors often have broad access. 💻
Encrypted Communication Channels
When sensitive discussions fly between teams and partners, standard email or messaging platforms leave data exposed—even if your network is locked down. Encrypted communication channels ensure that every email, chat, and file transfer remains unreadable to anyone except the intended recipient, regardless of where data travels.
Solutions like ProtonMail for email, Signal or Wire for messaging, and VeraCrypt for file transfers provide military-grade encryption (AES-256 or PGP) with zero access for providers. These tools integrate seamlessly with existing workflows while adding automatic key rotation and metadata stripping to prevent leaks. For compliance-heavy industries, HIPAA/GDPR-approved options like Thryv or Microsoft Purview offer audit logs to track access.
This safeguard is non-negotiable for legal, healthcare, and finance teams handling confidential client data. Even remote workers benefit from always-on encryption, ensuring sensitive emails or contracts stay secure whether sent from a café or a corporate server. 💻
Device Inventory and Compliance Tracking
Ever wondered how hackers slip through the cracks by exploiting devices you didn’t even know were connected? A device inventory and compliance tracking system solves this by maintaining a real-time catalog of every corporate device on your network—from laptops to IoT sensors—so only approved hardware gets access.
Tools like ServiceNow Asset Management or LANdesk automatically scan and classify devices, flagging non-compliant hardware before it becomes a breach entry point. They also enforce hardware compliance policies, ensuring devices meet security baselines (e.g., encrypted storage, up-to-date firmware). This layer is critical because 60% of breaches involve compromised endpoints—many of which are unmanaged rogue devices. ⚡
Incident Response Playbook Development
When a breach happens, every second counts—but most companies waste critical minutes scrambling to respond. An incident response playbook flips the script by defining pre-approved steps, clear ownership, and escalation paths before an attack even occurs, cutting containment time by up to 70% according to SANS Institute research.
Think of it as your cybersecurity battle plan: step-by-step procedures for detecting, isolating, and eradicating threats, complete with role-specific checklists (e.g., who calls law enforcement, who notifies executives, who triggers backup systems). Tools like Splunk ES or IBM QRadar integrate with these playbooks to automate alert triage, while tabletop exercises ensure your team practices responses annually. The playbook also maps legal and PR protocols, so you’re prepared for regulatory disclosures or customer notifications.
This isn’t just for enterprises—even small teams benefit from customizable templates (like those from NIST SP 800-61). Start with a phishing incident playbook, then expand to ransomware or insider threats. The goal? Zero panic, zero guesswork when seconds matter most. ✨